
The advertised monthly price of a dedicated server rarely tells the full story. Security add-ons — DDoS mitigation, hardware firewalls, intrusion detection, and SSL certificate management — are frequently sold separately, and their combined cost can add a meaningful layer to your baseline invoice. For teams that discover this after signing, the surprise is not just financial; it can also delay the security posture they assumed was included from day one.
This article breaks down each major security add-on category, explains what drives its price, and shows you how those costs stack up across different protection tiers. The goal is straightforward: give you a realistic monthly security budget figure before you commit to a contract, not after you receive your first renewal invoice.
Whether you are running a high-traffic e-commerce platform, a SaaS product, or infrastructure subject to compliance requirements, understanding security cost structure at the line-item level is the only way to compare providers on equal footing. It is also worth noting what this article does not cover.
Why Security Add-On Costs Catch Buyers Off Guard
Most dedicated server quotes advertise hardware first and leave security controls as optional line items. Buyers who compare only the base monthly rate often discover firewall, DDoS, IDS and certificate fees only after the first invoice cycle.
Providers structure security this way for a legitimate reason: protection requirements vary significantly by workload. A gaming platform facing volumetric attacks needs a different mitigation capacity than a small internal database server. Selling security as a modular add-on lets providers serve both without forcing every customer to pay for coverage they do not need.
The practical consequence for buyers, however, is that a plan advertised at a given monthly rate can look very different once even a baseline security stack is assembled. A hardware firewall license, a mid-tier DDoS mitigation package, and a managed intrusion detection service can each carry a separate monthly fee — and those fees are rarely displayed alongside the base hardware price during the ordering process.
By the time provisioning is complete, the true monthly security cost may represent a substantial share of the total invoice.
The gap between a bare plan and a minimally secured environment is where most budget surprises originate. Some providers bundle a basic level of network-layer DDoS filtering at no extra charge, while others charge incrementally for every protection tier above a low threshold. Knowing which model a provider uses — and what that threshold actually covers — is essential before signing.
The detailed comparison framework in Dedicated Server Add-On Costs – What Providers Charge Beyond the Base Plan maps those structural differences across the broader add-on landscape; the sections that follow here focus specifically on what each security layer costs and how to budget for it accurately.
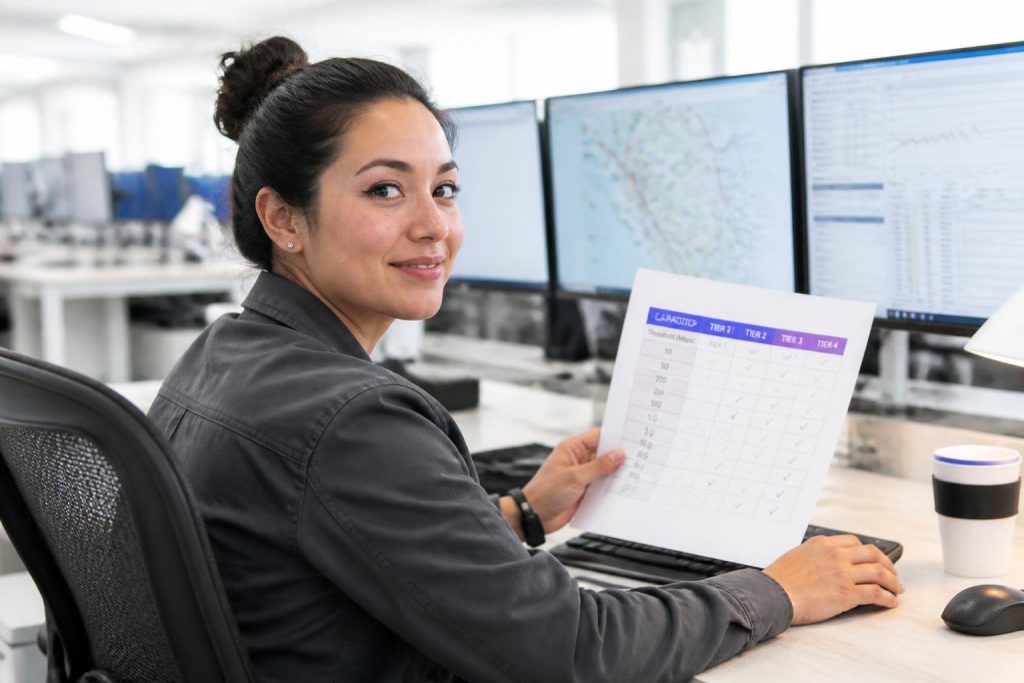
Matching your DDoS protection tier to your actual peak traffic and attack exposure prevents both overspending on unused capacity and costly gaps in coverage.
How to Budget for DDoS Mitigation Tiers
As noted under “Why Security Add-On Costs Catch Buyers Off Guard,” mitigation fees appear outside the base plan price — so the budgeting challenge is not discovering that cost exists but sizing it correctly before you commit to a tier.
DDoS mitigation tiers are priced by capacity and scrubbing depth. Budget from your realistic peak attack surface and required response time, then compare those requirements to the included baseline on the server plan before you buy an upgrade tier — keeping in mind that tier pricing is not linear, and the relationship between maximum attack volume, scrubbing capacity, and detection-to-mitigation latency is where buyers most often miscalculate.
Authentication does not itself protect an application from DDoS attacks. Determine whether the provider covers volumetric, protocol, and application-layer attacks, and use an application-aware service such as a reverse proxy or WAF where Layer 7 protection is required.
Basic network-layer filtering may be sufficient for a low-risk internal service, but public gaming, payment, and media platforms often require stronger protection. Evaluate expected attack vectors, protected protocols, scrubbing capacity, mitigation response, clean-traffic limits, and application-layer coverage instead of choosing a tier from server traffic volume alone.
Always-on scrubbing continuously routes traffic through the mitigation platform and therefore avoids the diversion delay associated with on-demand activation. However, attacks still need to be detected and classified, and mitigation effectiveness depends on the provider's rules, capacity, and response process.
Enterprise-grade mitigation, capable of absorbing very large volumetric attacks while maintaining low latency, is priced at a premium and is often negotiated rather than listed publicly.
What Hardware and Software Firewalls Actually Cost
Firewall protection on a dedicated server comes in two distinct forms, and the cost difference between them is substantial. A hardware firewall is a dedicated physical appliance provisioned at the network edge — before traffic ever reaches your server. A software firewall runs directly on the server's operating system and filters traffic at the host level.
PCI DSS requires network security controls that restrict traffic between trusted and untrusted networks and within the cardholder data environment where applicable. Those controls may be implemented with physical appliances, virtual appliances, cloud services, host-based controls, or a documented combination. A dedicated hardware firewall is not universally mandatory.
Both serve legitimate purposes, but they are priced on entirely different billing models, and confusing the two during the buying process is a common source of budget miscalculation.
Hardware firewalls are typically offered as a monthly rental add-on. The base fee covers the appliance itself, but rule-set management — the ongoing configuration, update, and audit of firewall rules — is frequently billed separately. Some providers include a standard rule set at no extra charge and charge only when you request custom rules or policy changes. Others bill a flat management fee regardless of how often rules are modified.
Software firewalls carry no hardware rental fee, but they consume server resources and require in-house expertise to configure correctly. If your plan includes managed support, firewall policy management may already be covered. If it does not, the labor cost of maintaining rules falls on your team.
Our dedicated server comparison resource breaks down which providers include managed firewall policy as part of their support tier and which treat it as a billable service — a distinction that can shift the real monthly cost considerably.
Knowing whether your provider bills per interface, per traffic volume, or as a flat managed retainer lets you accurately forecast intrusion protection costs before contracts are signed.
How to Calculate IDS and IPS Add-On Fees
Intrusion detection and prevention systems are priced on three primary models: per monitored interface, per volume of traffic inspected, or as a flat monthly retainer for a managed service. Understanding which model a provider uses before you sign is essential, because the same baseline protection can cost significantly different amounts depending on how your traffic profile maps to their billing structure.
A practical starting point is to request a sample invoice from the provider based on your expected throughput — not a list-price sheet. Providers whose billing scales with traffic volume can become unexpectedly expensive during legitimate traffic spikes, such as a product launch or seasonal surge, even when no attack is occurring. That distinction between attack-driven and growth-driven cost exposure is worth clarifying in writing before you commit to a contract.
Signature-based detection compares activity with known patterns, while behavioral or anomaly-based detection looks for deviations from an established baseline. Services that combine these methods may require additional processing, tuning, and analyst involvement and can therefore cost more. Compare detection coverage, tuning, retention, and analyst-response scope rather than assuming one universal pricing model.
When estimating your monthly spend, start with two figures: the number of network interfaces you need monitored and your average daily traffic volume. Providers that bill per interface charge a fixed fee per port, which makes costs predictable but can escalate quickly in multi-server environments. Volume-based billing is cheaper at low traffic levels but can spike unexpectedly during legitimate traffic surges — not just attacks.
A flat retainer simplifies forecasting but may include caps on log retention or the number of alerts a human analyst will investigate per month. Clarify those caps before committing, since alert investigation limits are a common source of unexpected overage charges.
SSL Certificate and TLS Management Costs to Include in Your Budgeting
SSL and TLS management costs extend well beyond the price of a single certificate. When you add up renewal tooling, wildcard licensing, and provider-managed installation, the total can reach several times the advertised certificate fee — and most of those charges appear nowhere in a plan’s headline price.
The certificate itself is only the starting point. A standard domain-validated certificate for a single hostname is often inexpensive or even free when issued through an automated certificate authority. The cost escalates when your environment requires broader coverage. Certificate cost depends on the issuer and validation model, not simply on whether the certificate is a wildcard. Automated certificate authorities can issue both single-domain and wildcard certificates without a certificate fee, although wildcard issuance normally requires DNS-based validation. Commercial OV, EV, support, warranty, or managed deployment services may introduce additional charges.
An organization-validated or extended-validation certificate adds identity verification steps that some providers charge a processing fee to complete on your behalf. If you run multiple distinct domains — common in agency or multi-brand e-commerce environments — a multi-domain certificate consolidates coverage but introduces its own licensing tier. Budget for the certificate type that matches your actual domain footprint, not the cheapest option available.
Renewal and installation fees are where the real markup often hides. Automated renewal through a provider's control panel may be included in a managed plan or billed as a separate monthly add-on. Manual renewal handled by a provider's support team typically attracts a one-time labor charge each cycle. If your server runs multiple virtual hosts, each requiring its own certificate binding, installation complexity rises and so does the associated fee.
Some providers also charge for TLS configuration audits — verifying cipher suites, protocol versions, and certificate chain integrity — which is a legitimate service for compliance-sensitive environments but should be itemized explicitly rather than bundled into an opaque "security management" line.
To avoid overpaying, confirm three things before signing: whether automated renewal is included or billed separately, whether wildcard and multi-domain licenses carry per-domain surcharges at renewal, and whether TLS configuration support is part of your managed tier.
Consolidating SSL management, threat monitoring, and response services under a single managed security package frequently delivers better value than assembling the same protection from separate vendors.
How Managed Security Services Change the Cost Equation
As noted under SSL Certificate and TLS Management Costs to Include in Your Budgeting, bundled managed security often costs less than building equivalent coverage piece by piece once staff time is counted.
A managed retainer never covers the vulnerabilities living inside your own code, no matter the price tag.
The decision point, however, is rarely that simple: contract length and exit terms frequently lock buyers into retainer structures that become expensive to unwind if workload or risk profile changes within the first year. Bundled managed security often costs less than building equivalent coverage piece by piece once staff time is counted.
The per-item approach looks cheaper on a line-by-line basis, but the labor required to configure, tune, and maintain each component independently often exceeds the managed premium within the first few months.
The more important cost variable is what a managed retainer explicitly excludes. Application-layer vulnerabilities inside your own codebase stay your responsibility regardless of how much you pay for managed security — a distinction that matters most when scoping the retainer against your actual exposure rather than assuming comprehensive coverage from a single contract.
What it typically does not cover is equally important to understand before signing. Most providers exclude application-layer security — meaning vulnerabilities inside your own codebase, your CMS configuration, or third-party plugins remain your responsibility regardless of the management tier you purchase. Custom compliance reporting, penetration testing, and forensic investigation after a confirmed breach are also commonly excluded or billed separately as project work.
Confirming the exact scope in writing prevents the assumption that "fully managed" means fully protected. The cost inflection point depends on team size and risk profile. A small technical team running a single production server may find that a managed security tier adds a meaningful but justifiable monthly premium over an unmanaged plan.
Hidden Security Costs That Inflate Your Monthly Invoice
The more operationally damaging pattern, however, is not the add-ons you declined — it is the charges attached to tasks you assumed your management tier already covered. These secondary costs share a common trait: they are triggered by normal security operations rather than exceptional incidents, which makes them difficult to forecast.
Remote hands labor, out-of-band management access, log retention beyond a baseline quota, and bandwidth charges related to scrubbing traffic can each appear on the same invoice without any single line item being large enough to prompt scrutiny. Cumulatively, they routinely exceed the cost of the firewall license itself.
- Remote hands fees for physical security interventions such as drive replacement or hardware security module swaps
- Out-of-band management access billed as an optional add-on rather than included in managed tiers
- Log retention charges that scale with storage volume beyond a baseline quota
- Incident response labor billed per hour when events fall outside a standard support scope
- Compliance reporting or audit log exports treated as billable professional services
- Bandwidth billing during and after DDoS mitigation (confirm whether attack traffic, clean traffic, or both is metered)
- Rule-set management fees charged separately from the base hardware firewall rental
Ask how the provider bills traffic during and after DDoS mitigation. Some providers exclude attack traffic, some meter only clean traffic delivered to the server, and others apply service-specific limits or overage rules. The contract must state which traffic is billable.
Remote hands fees are among the most common surprises.
When a security incident requires physical intervention — swapping a hardware security module, verifying a tampered drive, or replacing a network interface card — most providers bill this as an out-of-hours labor charge.
The rate varies by data center location and urgency tier, but it is almost never disclosed on the pricing page. Similarly, out-of-band management access — the dedicated connection that lets your team reach a server when the primary network is compromised — is frequently listed as an optional add-on rather than a default inclusion.
Without it, incident response during an active breach may require a remote hands visit, compounding both cost and downtime. IP reputation monitoring is another charge that surfaces unexpectedly.
If your server's IP address is flagged in abuse databases — due to a compromised application, a misconfigured mail relay, or a previous tenant's history — some providers charge for remediation, IP replacement, or delisting services. Others include basic monitoring but bill investigation and escalation separately.
A realistic security budget built before deployment eliminates the surprise expenses that erode margins after your server is already live.
How to Build a Realistic Security Budget Before You Sign
Begin by documenting the workload's exposure: public services, sensitive data, compliance scope, expected traffic, acceptable downtime, and internal response capability. This risk map determines which controls are required and which optional services can be introduced later.
Once you have that profile, work through each add-on category sequentially. Begin with the controls that protect availability — DDoS mitigation and firewall coverage — since downtime carries an immediate, measurable revenue cost. Add intrusion detection and log management next, particularly if your workload involves customer data or payment processing.
Two validation steps are worth building into your process before signing any contract. First, ask your provider to confirm in writing which quoted prices are promotional and which reflect the standard renewal rate, since introductory pricing on security tiers can reset significantly after the first term. Second, request itemized quotes for every add-on category — including remote hands rates, out-of-band access fees, and log retention limits — rather than relying on bundled plan descriptions.
Organizations subject to HIPAA or PCI-DSS requirements should note that compliance-specific charges such as audit logging, encrypted storage, and segmented network costs sit alongside these general security line items and require separate budget allocation.
Conclusion – Budget Security Costs Before You Sign, Not After
Security add-on costs are predictable — but only if you price them before you sign, not after the first invoice arrives. DDoS mitigation tiers, hardware firewalls, intrusion detection, SSL management, and secondary charges such as IP remediation and extended log retention each carry their own billing logic. Taken together, they can meaningfully widen the gap between a plan's advertised monthly rate and its true operational cost.
Mapping your risk profile before signing is what keeps a 36-month contract from delivering invoice surprises at renewal.
The discipline of mapping your workload's risk profile first, then pricing each security layer against that profile, is what separates a budget that holds over a 12-to-36-month contract from one that surprises you at renewal.




