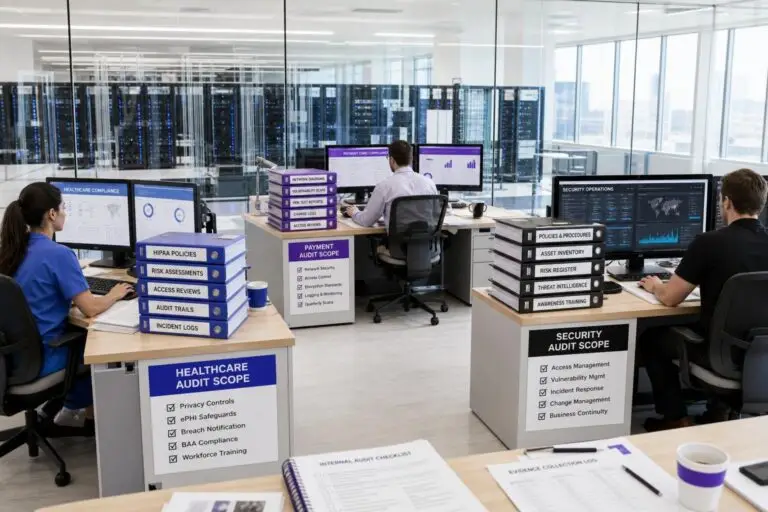

Organizations subject to HIPAA, PCI DSS, and SOC 2 often maintain overlapping controls and evidence separately. Without a shared control map, this can create duplicate policies, evidence requests, and remediation work.
The irony is that these frameworks share far more common ground than their individual documentation suggests, and a dedicated server is precisely the environment where that overlap becomes an engineering advantage rather than an administrative burden.
Dedicated, virtualized, and cloud environments can all support compliant workloads when responsibilities and controls are properly defined. Bare metal gives the customer direct control over more of the host, while managed services may shift some controls and evidence responsibilities to the provider.
It is the mechanism that lets you build one unified control set that satisfies all three frameworks simultaneously, rather than bolt-on controls after the fact. When your firewall rules, audit logs, and access policies are designed from the start to serve multiple frameworks at once, the evidence your auditors request is already organized and waiting.
What Is Dedicated Server Multi-Framework Compliance?
On a dedicated server, you hold complete authority over every configuration layer — the firewall, the logging pipeline, the access control model, the encryption stack — without negotiating boundaries with adjacent tenants or working around a hypervisor's constraints. On shared or virtualized infrastructure, portions of that control surface belong to the provider or the orchestration layer, which forces you to compensate through contractual mechanisms rather than direct technical implementation.
Differences in control ownership affect how evidence is collected, but they do not inherently require separate compliance workstreams. A shared control map can consolidate evidence across frameworks in bare-metal, virtualized, and cloud environments when responsibilities are documented clearly.
The three frameworks share substantial common ground at the technical layer: encryption requirements, access control obligations, audit log retention, and incident response documentation overlap to a degree that makes separate implementation genuinely redundant. A small, well-defined layer of framework-specific controls handles the remainder.
Nothing in that structure requires you to maintain three parallel evidence packages or run three separate remediation cycles when any framework updates its requirements.
The practical result is fewer total controls to maintain, faster evidence assembly before each audit window, and a shorter remediation cycle when requirements shift. Siloed compliance workstreams force engineering and security teams to duplicate policies, configurations, and evidence that already exist — multiplying overhead without improving the actual security posture of the underlying server.
This article shows you how to eliminate that duplication by treating the dedicated server's full-stack ownership as the architectural foundation the unified control set is built on, mapping concrete controls to all three frameworks simultaneously rather than managing each as a separate compliance project.
Siloing each regulatory framework into its own independent project forces teams to duplicate controls, documentation, and remediation cycles that a shared control architecture could handle once.
Why Treating Each Framework as a Separate Project Creates Redundant Controls
As noted under What Is Dedicated Server Multi-Framework Compliance?, a dedicated server gives you uncontested control over every configuration layer. The problem this section addresses is what happens when compliance teams fail to exploit that fact: instead of mapping one authoritative control set to multiple frameworks, they build three parallel documentation silos on top of identical infrastructure.
The cost accumulates not in the controls themselves but in the paperwork layer above them. Each framework receives its own access-control policy, its own audit-log retention schedule, and its own evidence package — all describing the same firewall rules, the same encryption stack, and the same access model.
The multiplier effect becomes acute the moment anything changes: a single firewall rule update or key rotation triggers three separate documentation revisions, three separate evidence submissions, and three separate auditor conversations, each referencing the same physical machine and the same underlying change.
A unified control mapping approach eliminates that multiplier at the source. When a single control record covers a concrete server-level configuration — MFA enforcement, TLS version policy, log retention period — and maps it simultaneously to the corresponding HIPAA, PCI-DSS, and SOC 2 identifiers, one remediation produces corrected evidence for all three frameworks in a single operation.
The sections that follow show exactly how to construct that mapping across the control categories where the three frameworks converge on your dedicated server.
How Control Overlap Between HIPAA, PCI-DSS, and SOC 2 Enables a Unified Architecture
Recognizing that overlap is the architectural prerequisite for eliminating redundant controls before the first policy document is written. The overlap is more extensive than most compliance teams realize when they first approach multi-framework programs — and the practical consequence is that a control gap in one framework is almost never isolated: it typically surfaces as a gap in two or three simultaneously, which means remediating it once closes the exposure everywhere.
A single control gap rarely affects just one framework — fix it once and all three audits benefit.
One implementation, three mappings, zero duplication.
Because a dedicated server exposes every configuration layer to direct inspection, auditors can verify HIPAA physical and technical safeguards against actual system artifacts rather than third-party attestations.
How Does Healthcare Compliance Map to a Dedicated Server Control Set?
That directness matters during an audit: an examiner can verify a control by inspecting a configuration file or a kernel audit log rather than relying on a shared provider's attestation.
One constraint worth planning for early is the physical safeguard requirement. Unlike the technical safeguards, which your own configuration can satisfy end-to-end, physical safeguard evidence for collocated or provider-hosted dedicated hardware must come from the provider — data-center access logs, cage entry records, and hardware disposal documentation are outside your direct control.
Confirming that your provider can produce this evidence in an auditor-ready format before you finalize your BAA is a decision point that technical mapping alone will not resolve.
The audit control requirement — §164.312(b) — calls for hardware and software activity to be recorded; on a dedicated server, kernel-level audit frameworks capture file access, privilege escalation, and authentication events in a format that auditors can examine without ambiguity. Transmission security under §164.312(e)(1) HIPAA requires appropriate safeguards for electronic protected health information in transit but does not prescribe a specific TLS version. The organization should select and document current, risk-appropriate transport encryption.
One area where your own configuration is not sufficient is physical safeguard evidence. For collocated or provider-hosted dedicated hardware, that evidence must come from the provider: data center access logs, cage entry records, and third-party audit reports covering physical security.
Requesting and retaining that documentation before an audit window opens is a compliance obligation your server configuration alone cannot fulfill.
How Network Segmentation on a Dedicated Server Shrinks Payment Data Scope
When the cardholder data environment is physically and logically isolated from every other workload on the machine, a qualified security assessor only needs to examine the systems that can reach cardholder data — not the entire server estate. That boundary decision is made at the configuration level, and it either holds or it does not.
A flat network where application servers, databases, and administrative interfaces share the same subnet gives an assessor no clean boundary to accept. A properly segmented environment gives them one.
The practical levers are VLAN boundaries, firewall rule documentation, and ingress/egress enforcement. On single-tenant hardware, you control each of these directly.
The critical compliance detail is documentation: every rule must carry a stated business justification, a creation date, and a named owner. Rules without that metadata are audit liabilities, not controls.
Ingress rules should permit only the specific ports and source addresses the payment flow requires; egress rules should be equally restrictive, blocking outbound paths that serve no documented purpose.
Scope reduction through segmentation is ultimately a documentation discipline as much as a technical one. The configuration creates the boundary; the written evidence proves it was intentional and maintained.
When access logs, change records, encryption evidence, and incident reports are collected from shared operational layers, a single evidence package can simultaneously close audit findings across all three frameworks.
Building a Unified Evidence Package That Satisfies All Three Audit Scopes
The key insight is that all three frameworks demand evidence from the same operational layers: who had access, what changed, how data was protected, and how incidents were handled.
Organizing evidence by control category instead of by framework can cut audit preparation costs dramatically.
Organizing those records once — in a format that maps to each framework's control language — eliminates the duplication that inflates audit preparation costs and introduces inconsistency between submissions.
The evidence categories that overlap across all three frameworks fall into four groups. Access and identity records cover SSH key inventories, privilege change logs, and multi-factor authentication enrollment records. Encryption attestations document full-disk encryption status, certificate validity periods, and key rotation timestamps. Change records capture every configuration modification with a business justification, an approver, and a completion timestamp.
Incident documentation includes detection timestamps, containment actions, and post-incident overview artifacts.
Collecting these records in one location — organized by control category rather than by framework — means a single pull satisfies all three audit scopes simultaneously. Dedicated Server Audit Logging — Build a Stack details how to structure the log collection layer that feeds this repository.
The organizational principle that keeps the package audit-ready year-round is continuous evidence capture rather than pre-audit collection sprints. The gap most teams face is not a lack of data but a lack of structure: records exist in disparate locations and formats that require manual assembly under time pressure.
Which Controls Remain Framework-Specific and Cannot Be Consolidated?
Not every compliance requirement maps cleanly onto a shared control. A meaningful portion of each framework’s obligations is genuinely unique, and conflating them with the unified control set creates gaps rather than efficiency. Identifying these residual requirements early allows your team to manage them as a discrete workload without disrupting the consolidated architecture built around the common core.
PCI DSS vulnerability scanning and penetration-testing obligations are located in Requirement 11, but their frequency, scope, and applicability differ. Map them to the exact PCI DSS version and validation method in use rather than assigning all of them to Requirement 11.3.
These residual controls require dedicated documentation tracks.
Programs built on bare metal most commonly collapse under the weight of undocumented scope creep, mismatched log retention periods, and provider documentation too vague to satisfy any framework's evidentiary standard.
What Pitfalls Derail Multi-Framework Compliance Programs on Bare Metal?
Three failure modes account for the majority of derailed programs: undocumented system interconnections that silently expand, log retention mismatches that create evidence gaps between frameworks, and provider-supplied documentation that lacks the specificity auditors require.
Undocumented interconnections are the most insidious pitfall.
Because dedicated server environments give teams full control over network topology, the responsibility for maintaining accurate, current system boundary diagrams rests entirely with the operator. Teams that treat their initial network diagram as a static artifact — rather than a living document updated with every configuration change — routinely discover scope expansion only when a qualified security assessor begins tracing data flows during fieldwork.
The Dedicated Management — Satisfying Payment and Auditors article addresses exactly how to capture these changes as auditor-ready records before scope drift occurs.
Log retention mismatches represent the second structural failure.
Aligning retention schedules to the longest applicable requirement across all active frameworks eliminates this gap without additional tooling.
Provider documentation is the third persistent failure point.
Unified Control Domains Across Three Compliance Frameworks on Dedicated Servers
| Criterion | encryption | logging | change |
|---|---|---|---|
| Encryption at rest | Satisfies all three frameworks under one implementation | Log access to encrypted volumes; no separate per-framework key store needed | Key rotation changes documented once, cited across all framework audits |
| Audit log scope | Encrypted log storage counts as a single control artifact for all auditors | Comprehensive logging covers access, integrity, and availability events across frameworks | Change events captured in same log pipeline auditors review for all frameworks |
| Change management evidence | Encryption config changes recorded in unified change record, not per-framework tickets | Log entries serve as timestamped evidence for change approval across all auditors | Single change management workflow produces artifacts acceptable to multiple auditors |
| Physical boundary control | Dedicated hardware eliminates shared-hypervisor risk; encryption applies to one physica… | Physical access logs from provider layer complement logical logs you control directly | Hardware-layer changes documented by provider; logical changes documented by operator |
| Segmentation requirement | Encrypted segments satisfy isolation objectives without separate per-framework VLAN sch… | Log traffic segmentation events once; evidence reused across all framework reviews | Network segmentation changes follow one change record cited in all audit packages |
Conclusion – One Control Set, Three Frameworks, Zero Redundancy
Building a multi-framework compliance program on a dedicated server is ultimately a design discipline, not a documentation exercise.
Compliance built on unified controls stays defensible as infrastructure evolves, while parallel silos inevitably drift.
The result is a leaner audit package, a shorter evidence-gathering cycle, and a compliance posture that remains defensible as your infrastructure evolves — because every control change is captured once and attributed to every applicable framework, rather than maintained in parallel silos that drift apart over time.




